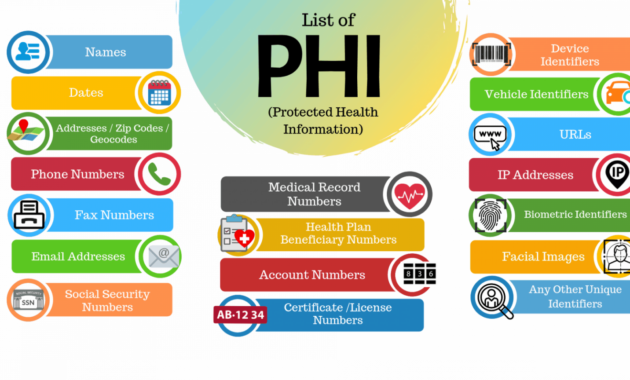

The Health Insurance Portability and Accountability Act (HIPAA) is a cornerstone of patient privacy in the United States. It establishes a framework for safeguarding sensitive health information. A foundational element of HIPAA is its definition of “healthcare provider.” This designation determines who is obligated to comply with the act’s stringent regulations, including those pertaining to the protection of protected health information (PHI). Understanding the scope of “healthcare provider” under HIPAA is crucial for ensuring comprehensive patient data security and adherence to federal law.
HIPAA broadly defines a healthcare provider as any individual or organization that furnishes, bills, or is paid for healthcare in the normal course of business. This definition encompasses a far-reaching spectrum of entities. It is not simply limited to physicians and hospitals. The key determinant lies in the entity’s involvement in providing or being compensated for healthcare services. This necessitates a deeper dive into specific categories and circumstances to fully grasp the breadth of this definition.
Direct Healthcare Providers: The Front Line of Patient Care
The most readily recognized category of healthcare providers under HIPAA includes those directly involved in patient care. This category includes:
- Physicians: Encompassing doctors of medicine (MDs) and doctors of osteopathic medicine (DOs), across all specialties, from general practitioners to cardiologists and surgeons.
- Dentists: Including general dentists, orthodontists, periodontists, and other dental specialists.
- Psychologists and Psychiatrists: Professionals providing mental health services, including psychotherapy, counseling, and psychiatric medication management.
- Chiropractors: Practitioners focused on the diagnosis, treatment, and prevention of musculoskeletal disorders, particularly those of the spine.
- Nurses: Including registered nurses (RNs), licensed practical nurses (LPNs), and advanced practice registered nurses (APRNs) such as nurse practitioners and certified nurse midwives.
- Physical Therapists: Professionals who help patients recover from injuries and illnesses through exercise, manual therapy, and other modalities.
- Occupational Therapists: Professionals who assist patients in performing daily living and work activities, addressing physical, cognitive, and emotional limitations.
- Speech-Language Pathologists: Professionals who diagnose and treat communication and swallowing disorders.
- Pharmacists: Professionals who dispense medications and provide drug information to patients and healthcare providers.
- Optometrists: Professionals who provide primary vision care, including eye examinations, vision correction, and the diagnosis and management of eye diseases.
This represents just a subset of the diverse array of direct healthcare providers subject to HIPAA regulations. Any healthcare professional who directly interacts with patients and handles their PHI falls under this category.
Institutions: The Infrastructure of Healthcare Delivery
Beyond individual practitioners, HIPAA also applies to a wide array of healthcare institutions. These entities are responsible for maintaining the confidentiality of patient information within their systems and processes. Key examples include:
- Hospitals: Including general hospitals, specialty hospitals (e.g., cardiac hospitals, cancer centers), and psychiatric hospitals.
- Clinics: Including primary care clinics, specialty clinics, urgent care centers, and community health centers.
- Nursing Homes: Providing long-term care and rehabilitation services to individuals with chronic illnesses or disabilities.
- Assisted Living Facilities: Offering housing and supportive services to individuals who require assistance with daily living activities.
- Rehabilitation Centers: Providing intensive therapy and rehabilitation services to patients recovering from injuries, illnesses, or surgeries.
- Laboratories: Analyzing biological specimens to diagnose and monitor diseases.
- Pharmacies: Dispensing medications and providing pharmaceutical services to patients.
- Home Health Agencies: Providing healthcare services in patients’ homes.
These institutions must implement comprehensive policies and procedures to safeguard PHI. They must also train their workforce on HIPAA compliance requirements.
Indirect Healthcare Providers: The Support Network
Interestingly, the HIPAA definition extends beyond those directly providing care to include entities that support the healthcare system. These indirect providers are often overlooked but play a critical role in the overall delivery of healthcare services. Examples include:
- Billing Services: Companies that process medical claims and payments on behalf of healthcare providers.
- Healthcare Clearinghouses: Entities that process nonstandard health information they receive from another entity into a standard format, or vice versa.
- Third-Party Administrators (TPAs): Companies that administer health benefit plans on behalf of employers or insurance companies.
- Business Associates: Any entity that creates, receives, maintains, or transmits PHI on behalf of a covered entity. This is a crucial distinction. Business associates are directly liable under HIPAA for violations of the Privacy and Security Rules. Examples include IT vendors, data storage companies, and consultants who have access to PHI.
The inclusion of these indirect providers highlights the interconnectedness of the healthcare ecosystem and the importance of securing PHI at every touchpoint.
Nuances and Exceptions: Navigating the Gray Areas
While the HIPAA definition of healthcare provider is broad, certain nuances and exceptions exist. For instance, an individual performing volunteer work at a hospital may not be considered a healthcare provider under HIPAA if they are not billing or being paid for their services. Similarly, a software company that develops electronic health record (EHR) systems but does not have access to PHI may not be considered a business associate.
The determination of whether an entity qualifies as a healthcare provider under HIPAA often requires careful consideration of the specific facts and circumstances. Consulting with legal counsel or a HIPAA compliance expert is recommended in cases where the applicability of the law is unclear.
Understanding the scope of “healthcare provider” under HIPAA is paramount for ensuring patient privacy and regulatory compliance. By recognizing the diverse range of entities subject to HIPAA regulations, we can collectively work towards creating a more secure and trustworthy healthcare system. The comprehensive nature of the definition underscores the commitment to protecting sensitive health information across the entire continuum of care. This vigilance is not merely a legal obligation; it is a fundamental ethical imperative that underpins the patient-provider relationship and safeguards the integrity of the healthcare system as a whole.